
Endpoint-native AI governance
What people put into AI, decided on the device.
A browser paste, prompt or upload is judged before it leaves. When the board, the auditor or the DPO asks, you answer with an inventory, a sentence per incident and a report, and no raw content left the laptop.
Transcript
Your people already use AI. Most of it, you can’t see. AI is no longer just a browser tab. It’s desktop apps, coding agents and MCP servers. Network tools see only some of these routes. Lamplighter sits on the device, where all four meet.
Someone pastes a patient referral into an AI tool. Lamplighter checks it on the laptop, before it lands. Nothing was sent. The person is told why, in your words. The letter never leaves the laptop. Lamplighter receives labels, counts and a hash. Never the text.
See every AI tool in use, and whose account it is. Approved or not, corporate or shadow, app by app. Every incident in one sentence, with no content in it. Coach first: people can give a reason to continue. Switch a rule to block when people know it.
Lamplighter. Complete AI endpoint control. Request a demo at lamplighterai.com.
Deploys and reports through the tools you already run
- Microsoft Intune
- Microsoft Purview
- Microsoft Sentinel
- Splunk
- Zscaler
- Netskope
- Cisco Umbrella
- Slack
- Teams
The problem
AI moved to the endpoint. The controls did not follow.
Staff paste confidential material into ChatGPT; that was settled in 2024. Since then coding agents, desktop assistants, local MCP servers and extensions that read chats have grown beneath the browser; a proxy sees the first two in part and the last two not at all.
of organisations now have agentic coding tools in use, up from 42% a year earlier. Local MCP traffic from these tools is invisible to network sensors.
Netskope AI report 2026of pastes into generative AI come from unmanaged, personal accounts. 22% of pastes carry personal or payment data.
LayerX, 2025 browser telemetryinstalls of two “AI assistant” browser extensions that harvested ChatGPT and DeepSeek conversations across more than 20,000 enterprise tenants.
Microsoft Threat Intelligence, Mar 2026added to the average cost of a breach with high shadow-AI involvement. 97% of organisations breached through AI lacked proper AI access controls.
IBM and Ponemon, Cost of a Data Breach 2025How Lamplighter is different
Network tools see none of the twelve routes to AI in full.
Our research scores four classes of sensor against twelve ways data reaches an AI tool from a workstation. A browser extension and an endpoint agent between them see nine of the twelve in full. Lamplighter is both, under one policy, and ships controls on five of the nine today.
A proxy sees the request after it has left the machine.
The extension holds a browser paste, prompt or upload until the device has decided; the decision budget is 100 ms. On Windows a paste into a desktop AI app is held the same way. Two local gateways, once you switch them on and point a tool at them, judge a coding agent's call and an MCP tool result by the same policy; the MCP gateway is in early access.
Which account, not only which site.
On eight of the most-used AI web apps the extension reads the vendor's own workspace signal and labels the account Corporate or Shadow; a work e-mail address alone does not make it Corporate. The same web address carries different retention and legal-discovery terms by account. Consumer chats were swept into court-ordered preservation in 2025; enterprise tiers were carved out. A domain list cannot tell them apart.
Three controls no other product reviewed documents in full.
On the device Lamplighter finds and reports MCP server configurations, local model runtimes and whether they are exposed to the network, coding agents run with permission checks off, and AI API keys on disk as provider, path and a four-character prefix. The last three are the controls no other product reviewed documents in full. Each is recorded and raised, not removed.
The ten requirements
Ten requirements any vendor can be held to, and where we stand on each.
The research sets out ten requirements for endpoint AI governance. Each bar is Lamplighter v0.18 against one of them, from an internal audit of its own code and tests.
Seven surfaces, 17 products
Seven places where data leaves a workstation for AI. Lamplighter has a control on all seven; no other product reviewed documents more than four.
Against the same 30 controls, Lamplighter v0.18 has 11 fully and 12 partly available today, 23 of the 30 in some form. The best-documented of the 17 products reviewed has 13 in full and 7 in part, 20 of the 30; the median product has 4 in full and 2 in part.
Said plainly, because you will check: the macOS agent does browser governance and discovery only, since the desktop paste and file gates are Windows features; releases are not yet code-signed; the external penetration test is scoped and not yet performed; and AI inside an approved product such as Microsoft 365 Copilot makes no distinct endpoint event, one of the four limits the research says no endpoint control closes on its own.
Vendor figures count what public documentation evidenced in September 2026; absence of documentation is not proof that a vendor lacks a capability. Lamplighter’s figures come from an internal audit of v0.18 against its code and tests, not from third-party review. Figure 2 and every score’s evidence: the research and the coverage page.
The product
Three pages from the dashboard. No content on any of them.
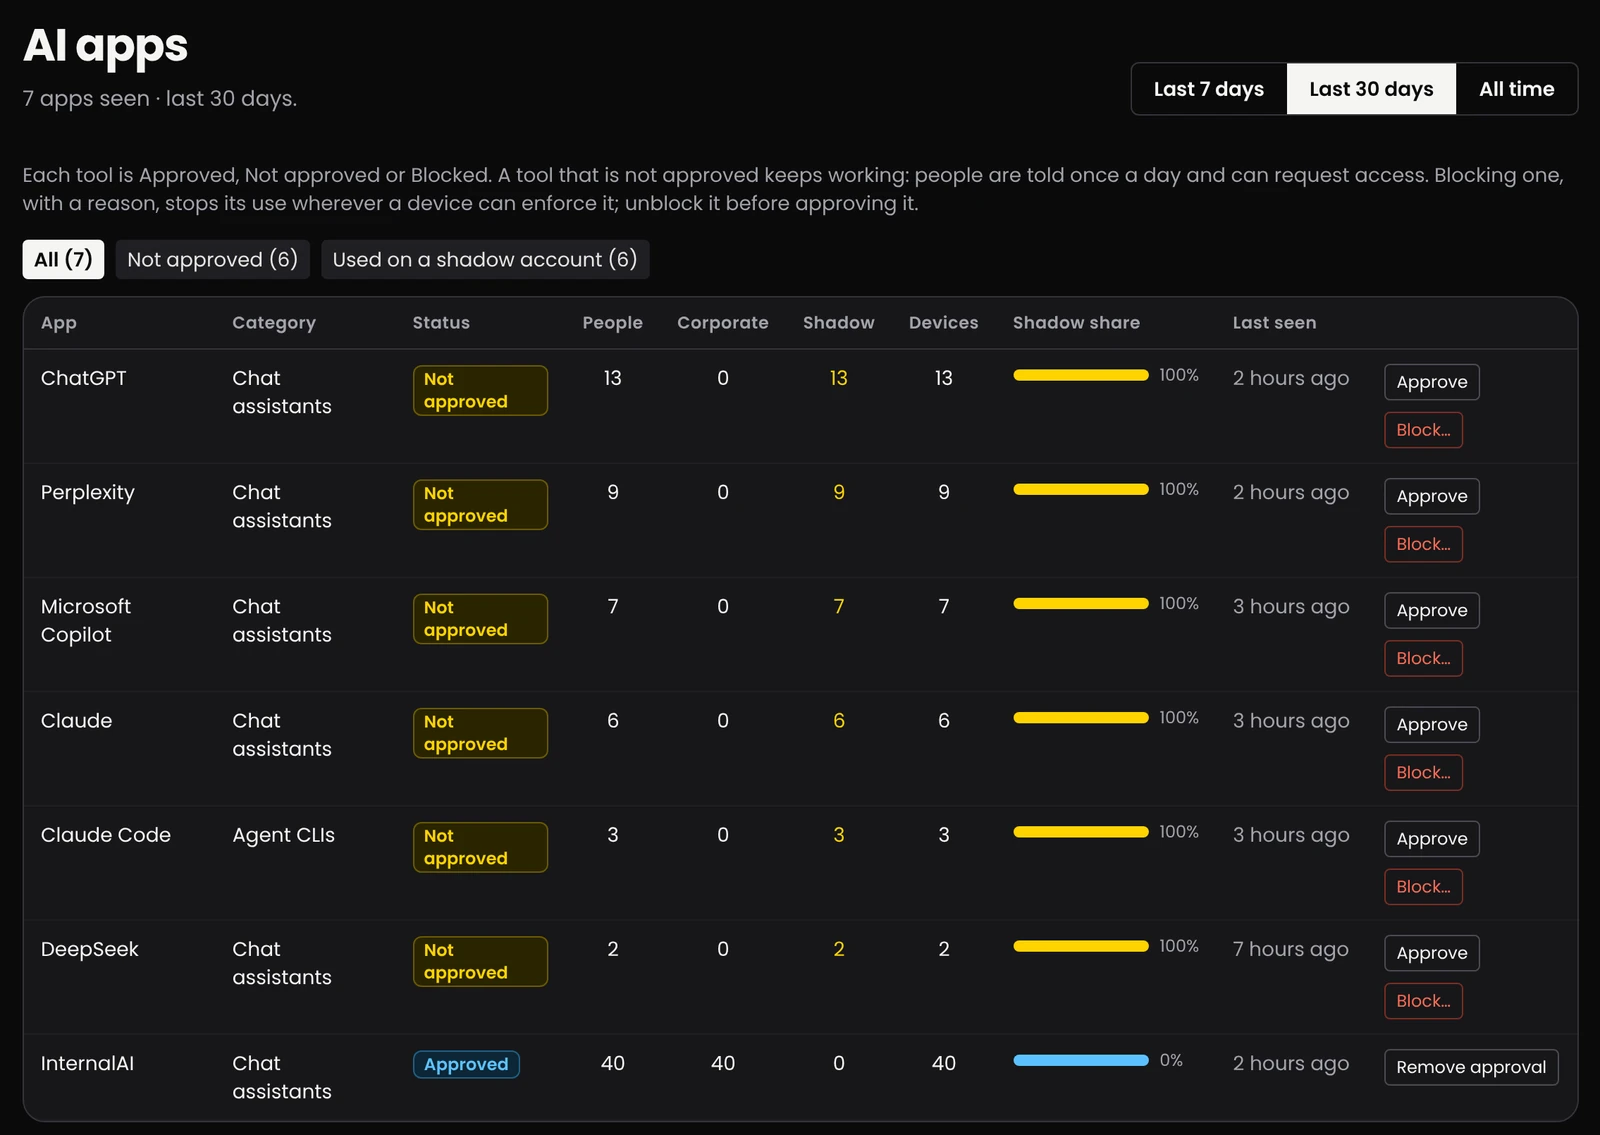
Every AI tool in use, Approved or Not approved
Each app: who uses it, on which accounts and devices, Corporate or Shadow. Approve or remove approval. Lamplighter reads your Purview labels and exports deny lists for AppLocker, Purview Endpoint DLP, Zscaler, Netskope and Umbrella.
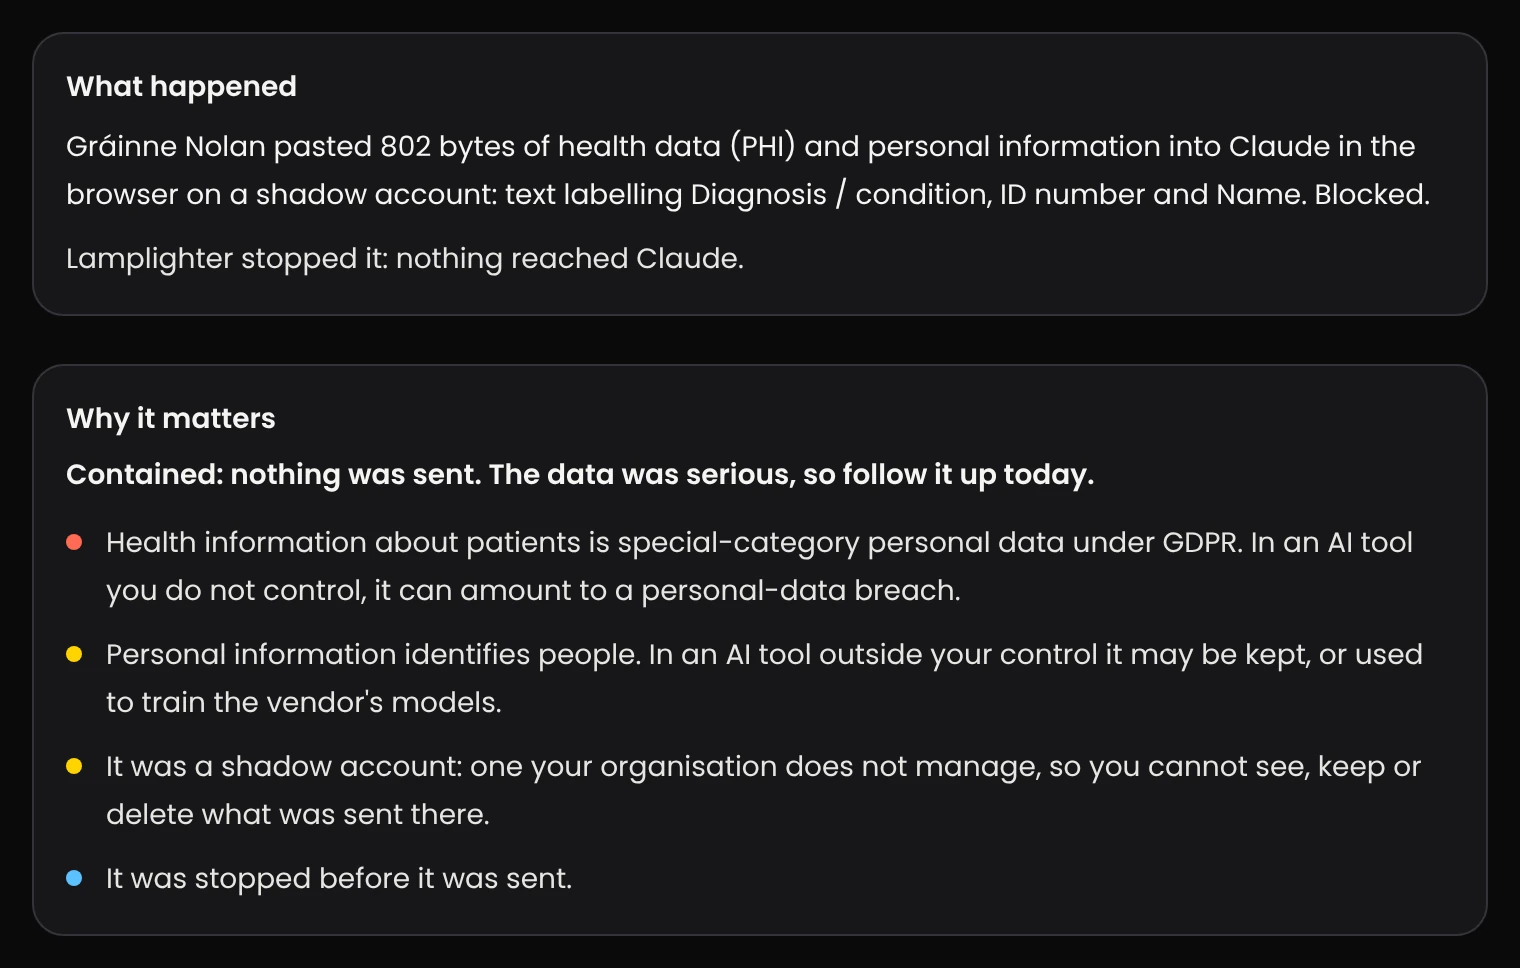
One incident, one sentence, no content
Who, what, how much, where, on which account: a person pasted health data into Claude on a shadow account. Blocked; nothing reached Claude. The gist gives the shape of the data, never the text.
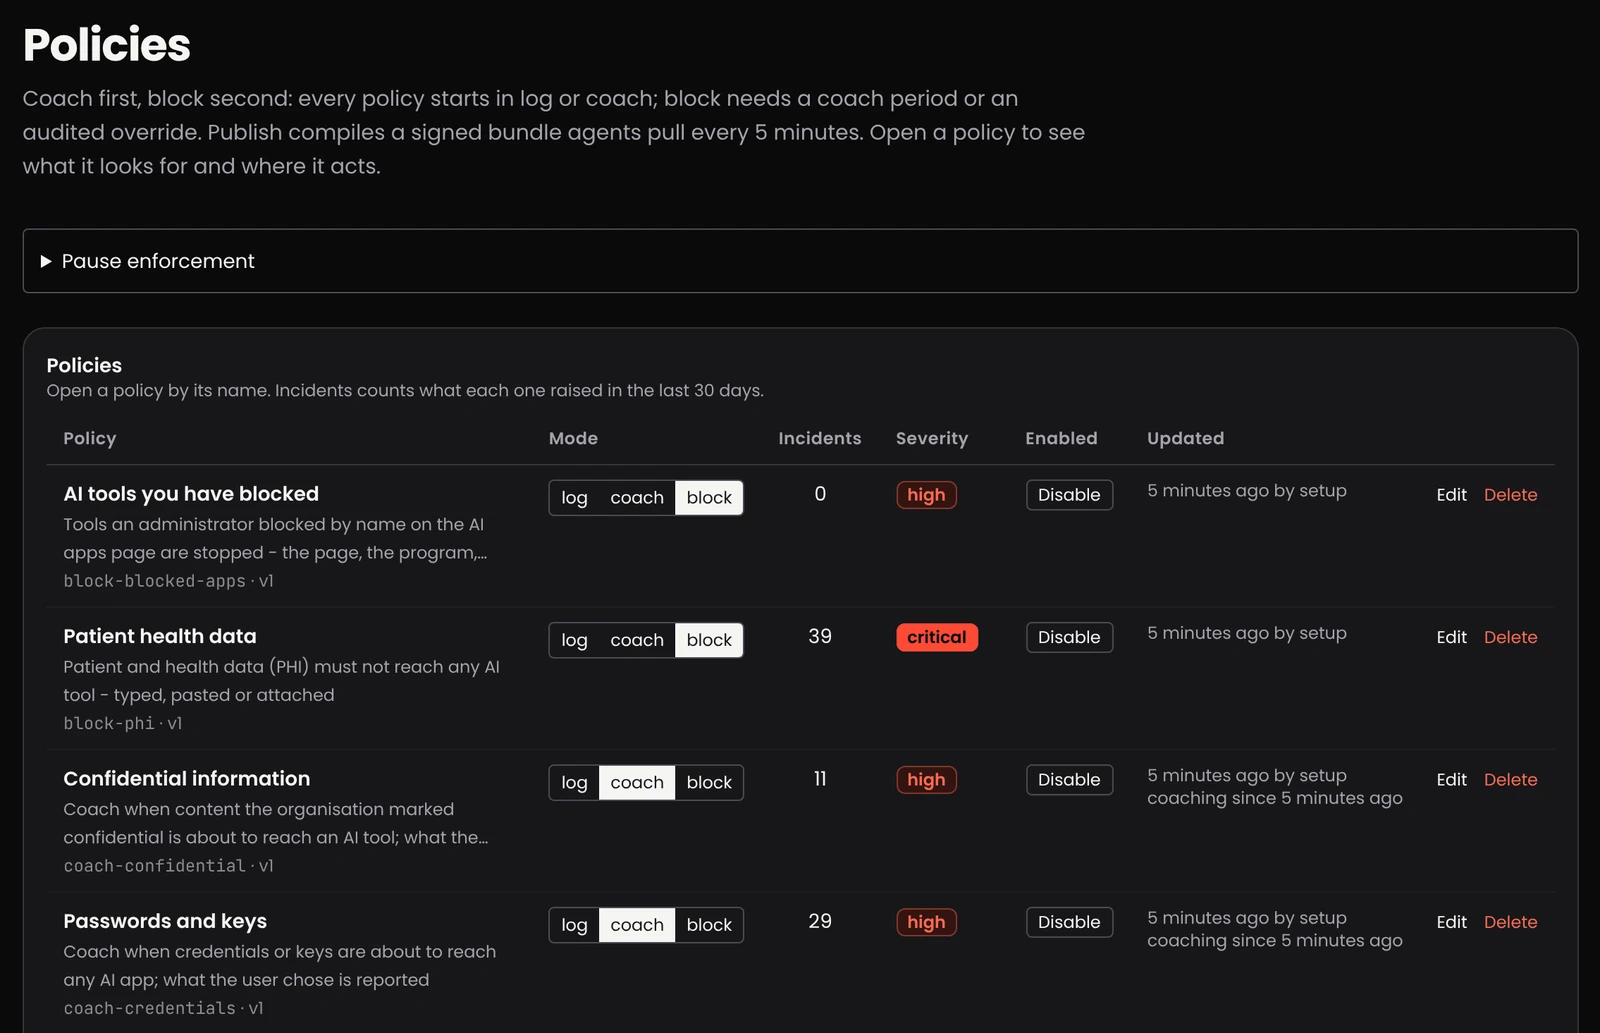
Log, then coach, then block
Every policy starts in log and moves to coach. Block waits for a seven-day coaching period unless an administrator records a reason. Simulate replays the last 30 days before you switch anything on.
For your DPO and works council
Raw content never leaves the device.
By default the dashboard receives who, which app, any reason they typed, labels, counts, hashes and a gist; tests hold that no word of the input is in it. A works council weighs metadata, not content. Every person sees the monitoring notice first. Our privacy impact assessment (GDPR Art. 6(1)(f), 88) is a template for your DPIA, not legal advice.
Start on your own devices. End with a report you can hand over.
EUR 5 per device per month, billed yearly, 25-device minimum, indicative until launch. A two-week pilot on a group of your own devices, against the policies you would run, ends with the posture report PDF. We set up the tenant; you push the MSI.