
Trust centre
Trust you can check, not trust you are asked for.
Lamplighter is a new company, and you should not take a new company’s word for anything. So this page puts each claim next to the way you can check it yourself, says plainly what is not finished, and names what no product like ours can do.
Verify it yourself
Three ways to check our main claim without trusting us.
The claim is that the text people type, paste and upload never reaches our servers. Here is how you can see that for yourself.
01 · Before you buy
Paste into this page and read the event
The panel below runs a copy of the first-tier validators in your browser and shows the event a device would send. It has the same fields as the real schema, and none of them can hold your text.
Try it belowevent.json // kind, app, account, bytes, // classes, gist, sha256, policy "text": // no such field
02 · During a pilot
Stream every event into your own SIEM
Send everything Lamplighter stores about your devices to Splunk, Microsoft Sentinel or a webhook, as JSON or CEF, and inspect it with your own tools. What you see there is every event we store.
Settings → SIEM export
splunk · sentinel · webhook
every stored event · JSON or CEF
03 · At any time
Download everything we hold about you
Your tenant owner can export every table we keep for your organisation, row for row, in a signed archive. Sealed credentials and live tokens are left out, and the manifest says why.
Tenant → Export
organisation.zip · NDJSON per table
signed manifest · digests per file
And on every device
Prove each machine is protected, and see when one stops being
A built-in device check runs eleven local checks with synthetic input and reports the result to your dashboard. Every device reports which protections are active. Removing the extension or the driver is recorded as a named tamper event, and a device that stops reporting shows as silent within 15 minutes rather than going quiet.
lamplighter selftest   // or "Run device check" on the device page
policy bundle · tier-1 model · tray helper · native messaging · extension
paste gate · driver · gateway · paste decision · file-open decision · upload
Try it
runs only in this pagePaste anything. See exactly what we would receive.
Nothing you type here leaves your browser. This page runs a simplified copy of the device’s first-tier validators, with a short word list standing in for the on-device classifier. The event on the right has the same shape as the one a device sends.
{
  "kind": "ai_app.paste",
  "ai_app": { "id": "chatgpt", "account_type": "personal" },
  "data": {
    "bytes": 217,
    "classes": [
      { "label": "financial", "confidence": 0.99, "detector": "tier0.payment_card" },
      { "label": "health", "confidence": 0.97, "detector": "page.word_list" },
      { "label": "pii", "confidence": 0.91, "detector": "tier0.labels" }
    ],
    "gist": {
      "shape": "prose",
      "placeholders": {
        "card_number": 1,
        "email_address": 1,
        "person_name": 1,
        "birth_date": 1,
        "identity_number": 1,
        "health_condition": 1,
        "medication": 1
      },
      "length_bucket": "<1k"
    },
    "content_sha256": "…"
  },
  "policy": { "matched": ["block-phi"], "decision": "block" }
}What your analysts see instead of content
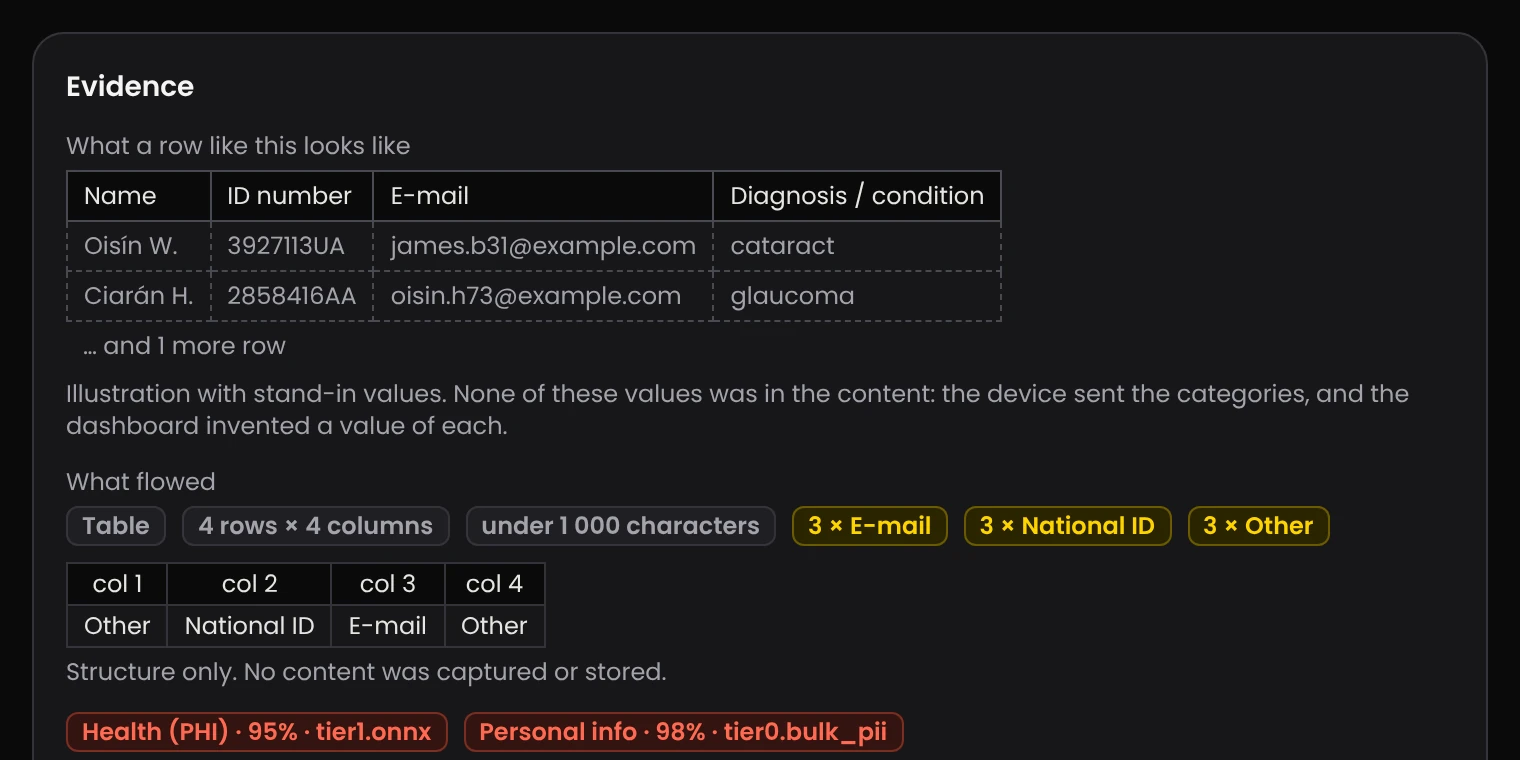
A picture of the shape, with values we invented.
When an analyst opens an incident, the dashboard draws what a row looked like using stand-in values: a wrong check digit, an example.com address, a common condition. It says so under the table. The device sent only the categories and the counts.
What we never do
Written into the product, and tested on every build.
These are rules in the code, not lines in a policy. Where a rule can be tested, an automated test fails our build if anyone breaks it.
No keystroke logging
A prompt is read when it is sent and a paste when it lands in an AI tool, never while someone types.
No raw content on our servers
What leaves a device is data types, confidence, counts, sizes, hashes and a summary with no words of the content in it.
No clipboard reading outside AI tools
The clipboard is only inspected when the paste target is a catalogued AI app.
No secrets kept when we find them
A key found on disk is reported as the provider, the path and its first four characters. Never the key.
No TLS interception
We never install a certificate to read encrypted traffic. API keys pass through the local gateway untouched.
No code of ours in the kernel
The only kernel component is a vendor-signed file driver, off unless you license it, and never on the paste path.
No training on your data
Our detection models are never trained on customer content, and our tests never use real company data.
No emotion inference
Nothing in Lamplighter scores how people feel. The EU AI Act prohibits it in the workplace.
No device before your notice
A device cannot enrol until your organisation has published a monitoring notice for staff.
No silent failure
If the decision pipeline is unavailable the device lets the action through, marks the event degraded, and your dashboard shows it.
Where your data lives
In the EU, in a database that is yours alone.
Every customer gets a separate database, and row-level security still applies inside it. The list of companies that process data for us is short, and a change to it is announced to you thirty days ahead.
- region
- Microsoft Azure, North Europe (Ireland)A tenant is created in one region and its data does not leave it
- isolation
- One database per customerRow-level security inside each, and tenant isolation tested in the data layer
- keys
- Credentials you give us are sealedAES-256-GCM, under a key that is itself held wrapped in Azure Key Vault
- retention
- You choose, from 1 day to 10 yearsDeletion is real deletion, on a schedule you can see
- sign-in
- Your own identity providerMicrosoft Entra ID or any OpenID Connect provider, by invitation, in four roles, with an optional second factor
- our access
- Only through a time-limited grantAt most 8 hours, never as owner, read-only unless stated, and written to your audit log as well as ours
Sub-processors
| Company | Service | What it processes | Where |
|---|---|---|---|
| Microsoft Ireland Operations Ltd | Microsoft Azure | Hosting, databases, storage, key management, monitoring and e-mail for the service | North Europe (Ireland) |
| Microsoft Corporation | Microsoft Entra ID | A dashboard user’s e-mail address and name at sign-in, and your directory where you connect Microsoft 365 | Per your Entra tenant |
Optional processors you choose and can remove at any time: an AI provider for incident summaries (redacted records only), your SIEM, and your alert channels. Our build fails if the deployment uses a service that is not on this list. The data processing agreement, the full sub-processor schedule and a privacy impact assessment template are available on request.
How it is built
Signed, isolated, and visible when something changes.
| Control | What it means | Status |
|---|---|---|
| Everything signed | Policies, the AI app catalogue, detection models and agent update manifests are signed, and every device verifies them before use. Updates roll out in rings that halt on a regression. | Available |
| Device certificates | Each device enrols with its own certificate from your organisation’s own certificate authority, and a revoked device cannot report. | Available |
| Tampering made visible | Removing protection raises an alert, and uninstalling needs a token your organisation holds. | Available |
| Roles and an audit log | Viewer, analyst, admin and owner, with every admin action recorded. | Available |
| Sealed evidence on devices | Optionally, and only behind a recorded legal sign-off, what was attempted at a coach or block is sealed on the device to a key only your organisation holds. We cannot open it. | Available |
| Signed installer | Release packages are not yet code-signed. Signing is built into the release pipeline and awaits its certificate. | In development |
| Independent assurance | An external penetration test, with its scope written, then a formal audit. | Roadmap |
How detection is tested
We publish what our detection misses.
No independent benchmark exists for this kind of detection, and every precision figure in the market is the vendor’s own. So here is ours, including the weak spots. Each technique below disguises a sensitive sample; the score is the share still caught.
| Evasion technique | Validators alone | With the on-device classifier |
|---|---|---|
| Extra spacing inside numbers | 0.79 | 1.00 |
| Zero-width characters | 0.00 | 0.94 |
| Look-alike letters (homoglyphs) | 0.40 | 0.96 |
| Base64 encoding | 0.00 | 0.43 |
| Hex encoding | 0.00 | 0.86 |
| Split across chunks | 0.80 | 1.00 |
| Hidden in a code comment | 1.00 | 1.00 |
| CSV inside JSON | 1.00 | 1.00 |
Golden suite v1: synthetic samples only, 15 per data class, run on every build. Base64 is the known gap. Images are not checked yet.
Limits
What no endpoint control can do, ours included.
Exfiltration from the AI vendor’s cloud
In one documented case, hidden instructions in an e-mail made a cloud research agent send personal data to an attacker from the vendor’s own servers. No endpoint or network control could see it. What we do: govern connectors and catch the links that start such chains.
Unmanaged devices and phones
Lamplighter instruments managed computers. Blocking is known to push some use to phones. What we do: pair with tenant restrictions, conditional access and single sign-on, which are the controls for that gap.
Vendor retention and training
How long a vendor keeps a chat, whether it trains on it and whether a court holds it are invisible to any endpoint. What we do: identify the app, account and edition in use, which decides which terms apply.
AI inside approved SaaS
AI features running inside an approved product, against data the vendor already holds, make no distinct endpoint event. What we do: point you to that vendor’s own audit and compliance interfaces.
The honest claim is everything needed at the endpoint, plus a named connector-governance and vendor-selection process, plus an API plane for approved platforms.The endpoint is the new AI perimeter, section 5
And our own limits today
What Lamplighter v0.18 does not do yet.
From section 7.4 of the white paper. Worth knowing before a procurement decision, not after.
| Limit | What it means for you |
|---|---|
| macOS is discovery and browser only | The desktop paste gate, file-open control, clipboard provenance and OCR are Windows features today. |
| Remote sessions bypass the paste gate | A paste inside Remote Desktop, Azure Virtual Desktop, Windows 365 or Citrix is not seen. The device is reported as unprotected for that session rather than shown as covered. |
| Accounts are read on eight AI web apps | Other apps, and all desktop and command-line use, read as Shadow. Confirming Corporate against your own registered domains is on the near-term roadmap. |
| Gateways are opt-in | Coding agents are inspected only once each tool is pointed at the local gateway; a tool that is not is reported, not inspected. The MCP gateway covers local servers in users’ JSON configurations. |
| The file driver is optional | Blocking a file an AI app opens needs a separately licensed third-party driver, off by default, with its licence installed on each device by hand for now. |
| Store listing not yet published | Fleets managed only through Entra ID and Intune need the browser-store listing to force-install the extension. |
| Firefox and Linux | On the roadmap. |
Leaving
Easy to try, and just as easy to leave.
Take everything with you
A signed export of every table we hold for you, whenever you ask.
Then we delete it
Your database is dropped after a 30-day period in which you can change your mind.
Devices put things back
Uninstalling restores every AI tool configuration Lamplighter changed, byte for byte.
Nothing left running
Uninstall removes the service, the extension policy and the evidence held on the device.
Bring your security questionnaire.
We will answer it with the architecture, the privacy impact assessment, the data processing agreement and the people who built it.